3. Specifications:
3.7 Security of network equipment
Since cybercrime is a constant and growing threat, it is necessary to guard against potential attacks.
That is what we are going to cover in this section...
2 options depending on the equipment:
First method: (less secure)
enable secret <password>enable is the command used to connect in privileged mode
secret makes it possible not to display the password in clear text in the configuration of the equipment and uses an md5 hash by default
There is also a hashing method stronger than md5, which is sha256.
I recommend setting up sha256 whenever possible.
Second method (more secure)
enable secret .... à vous de faire !This command is used to set a password for the network equipment
sha256 (Secure Hash Algorithm) is a hash function used to secure information such as a password.
For access by technicians, a user has been created:
username tech secret <password>
username tech privilege 15
The username command is used to create or manage the user,
The privilege argument is used to associate the level of rights, 15 being the maximum level
It is possible to search the configuration for a specific item with the argument include <search>
do sh run | include tech
Here we searched for tech in the "running-config".
The configuration called running-config is the active configuration used when the network equipment is started.
It is very important to check access to the various network interfaces with the command:
sh line
We observe the interfaces:
- CTY = console port
- AUX = auxiliary port
- VTY = virtual ports
It is ESSENTIAL to assign a password on the console interface:
conf t
line con 0
password <password>
login
line con 0 is used to select the console port
password is used to set the password
login will make the password mandatory at connection
If we want to use the users created earlier when connecting, it is necessary to use
login localIt is up to you to set the password for line aux 0
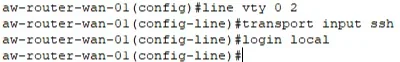
If we want to allow remote administration of our network equipment, we will have to use a protocol such as SSH, which makes it possible to establish a secure shell communication.
Prerequisites:
- Create a user and a password
- Define a domain name as well as a host name
- The equipment supports SSH
To define the domain name on the equipment:
ip domain-name awoui.frThen the host name:
hostname aw-router-wan-01To be able to generate a secure key for SSH:
crypto key generate rsaIt is worth putting ssh in its latest version:
ip ssh version 2Defining the SSH access lines:
Selecting the virtual lines:
line vty 0 2You have to indicate that ssh will be used on these lines:
transport input sshAs seen previously, we can use the users created for the connection:
login local